Impact Managed Compliance
Keep Your Compliance Program Running.
Getting compliant is only the beginning. Policies need to stay current, risks change, controls need to operate, evidence needs to be maintained, vendors require review, and audits and customer requests continue throughout the year.
Impact Managed Compliance provides ongoing, hands-on support to help keep your compliance program operating, current, and ready.
More Than a Gap Assessment
We Don't Just Identify Gaps. We Help You Address Them.
Impact Managed Compliance is designed to provide hands-on support, not simply identify compliance gaps and leave your team with a list of things to fix.
Depending on your service level, Impact Risk Advisors helps perform risk assessments, conduct vendor diligence, develop and maintain tailored policies, monitor controls and evidence, manage remediation, prepare for audits, respond to security questionnaires, and keep the compliance program moving throughout the year.
When remediation requires technical implementation, we work with your internal IT team or technical provider to define the requirement, support the remediation process, validate implementation, and track the issue through resolution.
We don't just monitor controls. We help you operate and improve the compliance program behind them.
Impact Maintain
Support for Your Internal Compliance Owner
For organizations that have someone internally responsible for compliance but need experienced support maintaining the program.
Starting at $1,000/month
Impact Manage
Your Outsourced Compliance Function
For organizations that want Impact Risk Advisors to take a more active role managing the ongoing compliance program and provide greater access to experienced compliance and security leadership.
Starting at $1,750/month
| Included Service | Impact Maintain | Impact Manage |
|---|---|---|
| Compliance Calendar | Included | Included |
| Annual Risk Assessment | Included | Included |
| Risk Register Review & Maintenance | Included | Included |
| Tailored Policy Review & Updates | Included | Included |
| Control Design & Improvement Support | Included | Included |
| Control Monitoring | Quarterly | Monthly |
| Evidence Review | Quarterly | Monthly |
| Remediation / POA&M Tracking | Quarterly | Monthly |
| Vendor Due Diligence | Up to 5/year | Up to 15/year |
| Security Questionnaires | Up to 4/year | Up to 10/year |
| Audit Readiness Support | Included | Included |
| Compliance & vCISO Advisory Hours | Up to 8 hrs/year | Up to 40 hrs/year |
| GRC Platform Administration | Add-on | One Platform |
| Compliance Review Meetings | Quarterly | 30 min/month |
| Compliance Status Summary | Quarterly | Monthly |
Compliance & vCISO Advisory Hours
Included advisory hours may be used for auditor meetings and requests, customer compliance discussions, security and compliance governance, management guidance, risk and control decisions, remediation guidance, security program planning, and other related compliance and security advisory needs.
Technical implementation and engineering activities are not included.
Compliance Review Meetings
Compliance review meetings are used to discuss program status, upcoming compliance activities, open remediation items, control or evidence issues, vendor and customer requests, audit matters, and management actions or decisions requiring attention.
Impact Maintain includes quarterly compliance review meetings.
Impact Manage includes one 30-minute compliance review meeting each month.
Compliance Status Summary
The Compliance Status Summary provides management with a concise view of the compliance program, including applicable upcoming activities, open remediation items, significant risk or control matters, vendor and questionnaire activity, audit readiness, and items requiring management attention.
Impact Maintain receives a quarterly status summary.
Impact Manage receives a monthly status summary.
Security Questionnaire Note
Additional standard security questionnaires beyond the annual allowance are available for $240 each.
Extensive or unusually complex questionnaires may require separate pricing based on scope.
Vendor Due Diligence Note
Included vendor due diligence covers standard security and compliance reviews of vendors, including review of available assurance documentation, identification of relevant risks or gaps, and follow-up items where applicable.
Vendor reviews beyond the annual allowance are available separately based on volume and complexity.
Clear Scope. Predictable Support.
Impact Managed Compliance starting prices are based on one primary compliance framework, organizations with 1–20 employees, one primary in-scope environment, and typical small-business technology and operational complexity.
Additional frameworks, SOC 2 Trust Services Categories, entities, environments, significant increases in vendor volume, extensive security questionnaires, complex infrastructure, or other material increases in scope may require adjusted pricing.
Standard framework scope generally includes:
- SOC 2: Security Trust Services Category
- HIPAA: HIPAA Security Rule
- GLBA: FTC Safeguards Rule
- NIST: One agreed NIST SP 800-53 Rev. 5 control baseline for one defined in-scope environment
- ISO 27001: One defined ISMS and certification scope
Additional Services & Client Benefits
Additional Resources When You Need Them.
Managed Compliance clients can also access additional compliance, security testing, technology, and independent audit resources as their needs evolve.
| Additional Service | Managed Compliance Client Benefit |
|---|---|
| GRC Platform | Access to preferred partner pricing where available for supported GRC platforms. Software licensing is separate from the Managed Compliance service. GRC platform administration is included with Impact Manage for one platform and available as an add-on to Impact Maintain. |
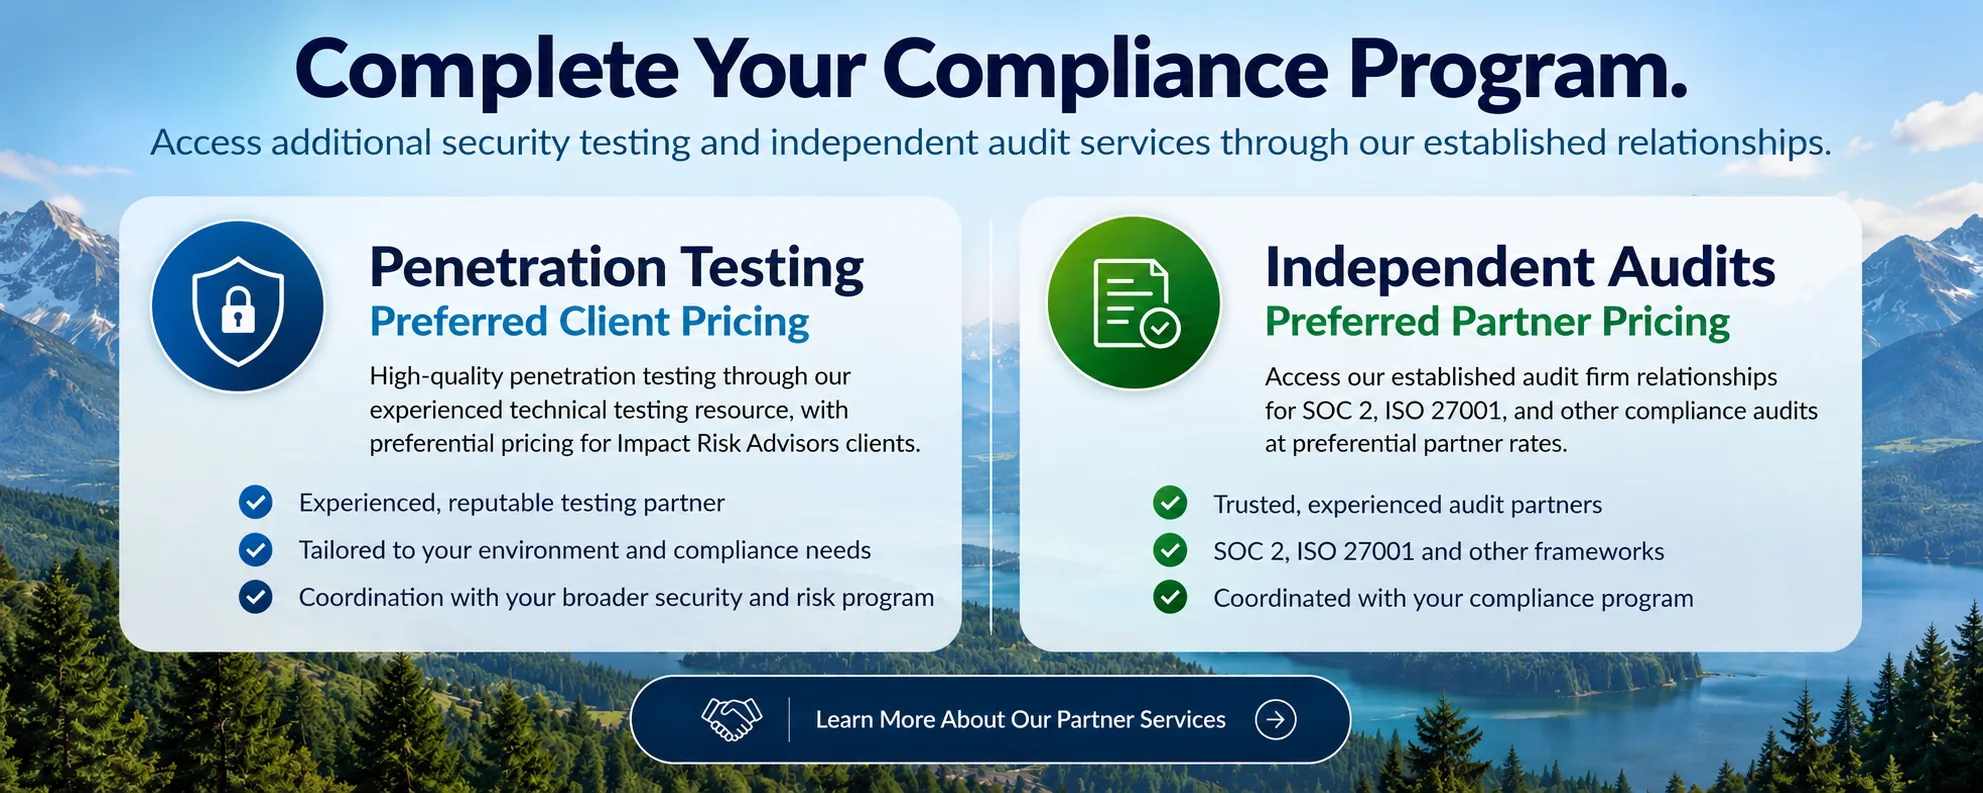
| Penetration Testing | Access to penetration testing at preferred client pricing, coordinated with your broader compliance and risk requirements. |
| Independent Audits | Access to established audit firm relationships and preferred partner pricing for SOC 2, ISO 27001, and other applicable independent audits. |
| Additional Security Questionnaires | Additional standard questionnaires beyond the included annual allowance are available for $240 each. Extensive or unusually complex questionnaires may be quoted separately. |
| Additional Vendor Due Diligence | Additional vendor reviews beyond the included annual allowance are available based on volume and scope. |
| Additional Compliance Frameworks | Additional frameworks can be incorporated into the Managed Compliance program based on scope and complexity. |
| ISO 27001 Internal Audit | Independent ISO 27001 internal audit services are available separately for initial certification and surveillance cycles. |
Ongoing Compliance Management
Compliance Is a Continuous Process.
Impact Managed Compliance helps keep the activities behind your compliance framework moving throughout the year.
- 1
ASSESS
Evaluate requirements, risks, changes, and the current state of the compliance program.
- 2
DESIGN
Develop and improve policies, controls, processes, and supporting documentation based on your actual environment.
- 3
OPERATE
Perform scheduled compliance activities, monitor controls, maintain evidence, review vendors, and keep required documentation current.
- 4
REMEDIATE
Track identified gaps, findings, and control issues and work with responsible teams to move remediation toward completion.
- 5
VALIDATE
Review evidence, validate implementation, support audit preparation, and help address auditor or customer requests.
- 6
MAINTAIN
Keep the compliance program current as systems, vendors, risks, requirements, and the organization change.
GRC Platform Flexibility
Use Your Platform. Add One. Or Don't.
A GRC platform can make compliance management more efficient, but it should support the compliance program, not define it. Impact Managed Compliance can work with the technology approach that makes sense for your organization.
Already Have a GRC Platform?
We can work within your existing platform to manage controls, evidence, risks, policies, remediation, and other compliance activities.
Want a GRC Platform?
We can help evaluate and implement an appropriate platform and provide ongoing administration based on your Managed Compliance service level.
Managed Compliance clients may also have access to preferred partner pricing for supported platforms.
Software licensing is separate.
Don't Need a GRC Platform?
That's fine too.
We can manage the compliance program using a structured compliance workspace and defined processes for controls, evidence, risks, policies, vendors, remediation, and compliance activities without requiring an expensive dedicated GRC platform.
Practical Compliance Support
Built Around the Work That Actually Needs to Get Done.
Hands-On Support
We don't simply identify gaps. We help manage the compliance work needed to address them and track issues through resolution.
Tailored, Not Generic
Policies, risks, controls, and compliance activities are based on your actual organization, systems, operations, and requirements rather than a generic template library.
Experienced Guidance
Managed Compliance includes access to experienced security, audit, risk, and compliance guidance, including defined vCISO advisory hours within each service level.
Technology Flexible
Use your existing GRC platform, add one when it makes sense, or operate without one. The compliance program comes first.
Keep Your Compliance Program Moving.
Whether you need experienced support for your internal compliance owner or want Impact Risk Advisors to take a more active role managing the program, we can help keep your compliance activities moving throughout the year.
Schedule a ConsultationWe'll discuss your existing compliance program, current responsibilities, framework requirements, and the level of ongoing support that makes sense for your organization.