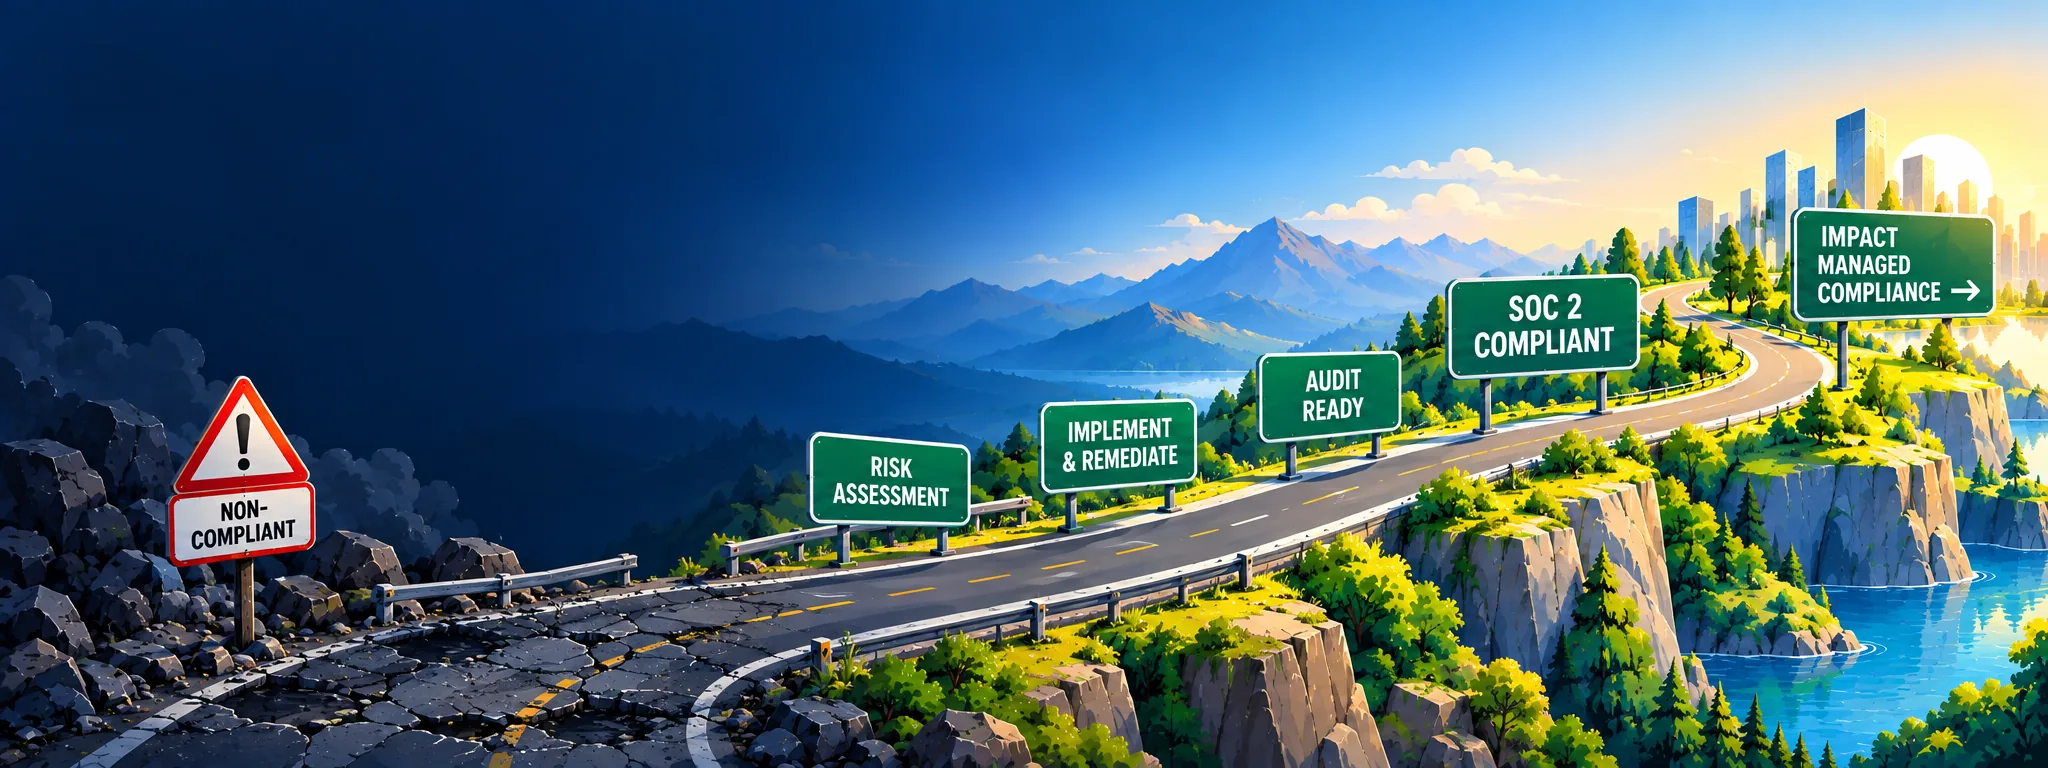
The compliance road: from Non-Compliant through Risk Assessment, Implement & Remediate, Audit Ready, and SOC 2 Compliant to Impact Managed Compliance

Practical Compliance. Real Impact.

Get Compliant.
Stay Compliant.

Impact Risk Advisors helps organizations build, implement, and maintain practical cybersecurity compliance programs across SOC 2, ISO 27001, HIPAA, NIST, and GLBA.

Whether you need to establish a compliance program or keep an existing program operating, we provide experienced support from initial readiness through ongoing compliance management.

SOC 2|ISO 27001|HIPAA|NIST|GLBA

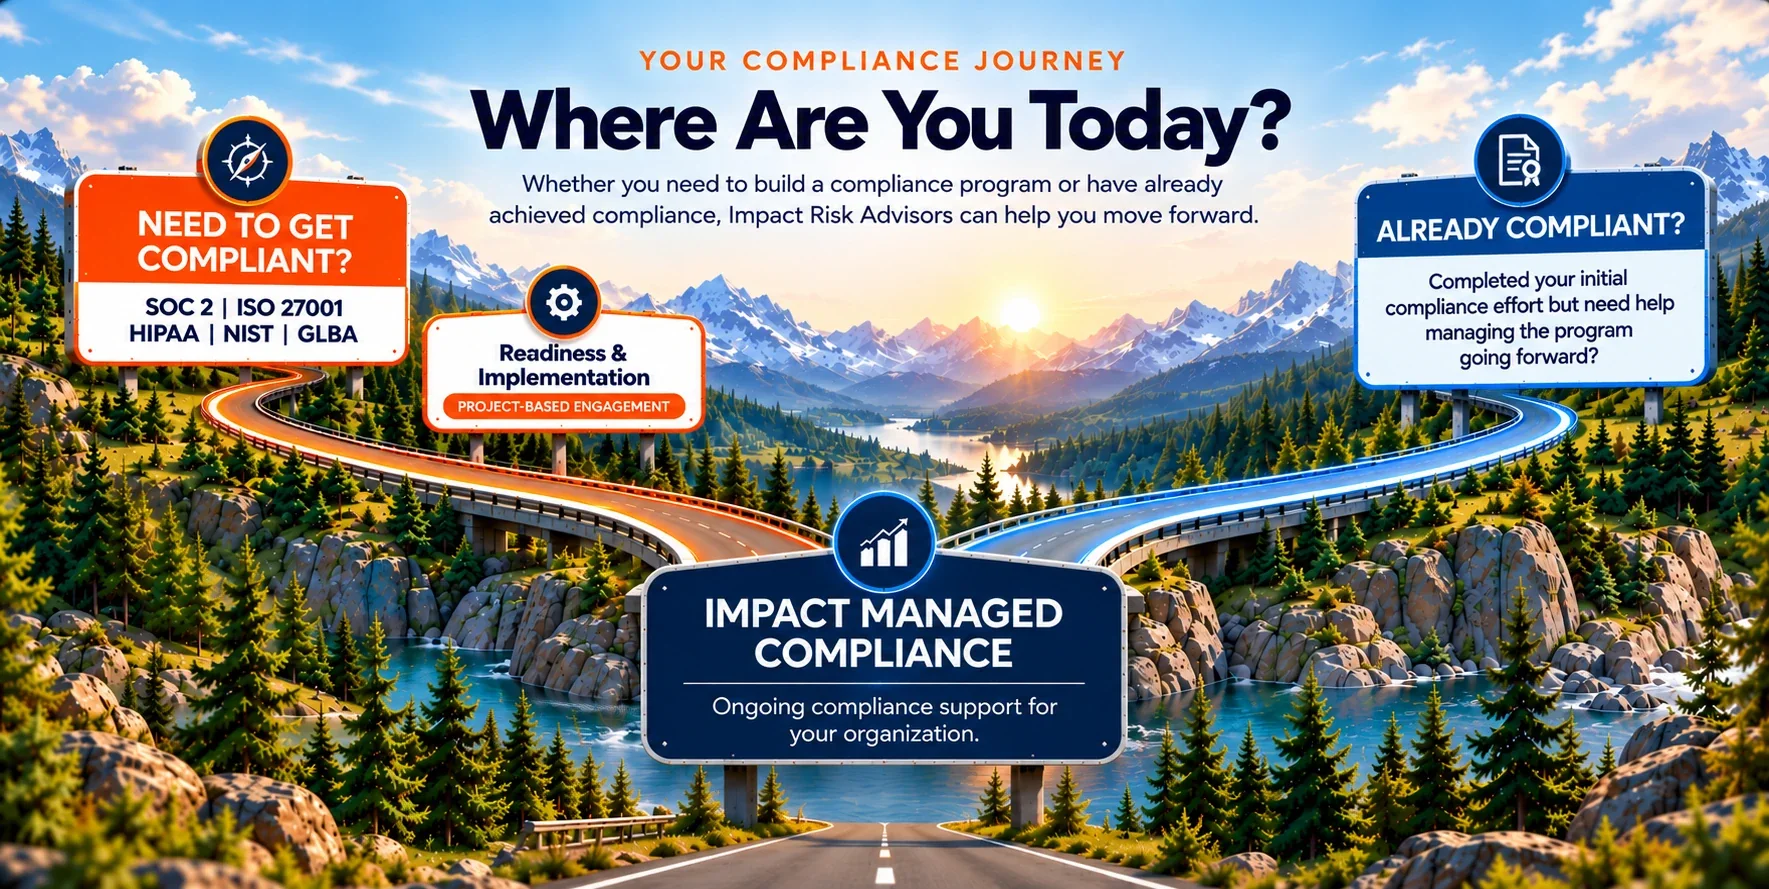
Your compliance journey - Where are you today? Organizations that need to get compliant (SOC 2, ISO 27001, HIPAA, NIST, GLBA) move through Readiness & Implementation, a project-based engagement. Organizations that are already compliant and need help managing the program going forward go directly to Impact Managed Compliance. Both paths lead to Impact Managed Compliance: ongoing compliance support for your organization.

Already Compliant or Just Getting Started?

See what's included in Impact Managed Compliance and view pricing by framework.

View Managed Compliance Pricing

Readiness, Implementation & Internal Audit

Build the Right Compliance Program From the Start.

Impact Risk Advisors helps organizations assess requirements, identify gaps, develop policies and controls, manage risk, address readiness issues, and establish the documentation and processes needed to operate an effective compliance program.

Implementation services are tailored to your actual environment rather than built around generic policies and checklists.

Readiness & implementation

SOC 2Security Implementation

SOC 2 Security readiness and implementation, including scope definition, gap assessment, risk assessment, policy and control development, remediation guidance, evidence requirements, and audit readiness.

Starting at$16,500One-Time Implementation Project

Standard Scope: SOC 2 Security Trust Services Category only.

Learn About SOC 2
Readiness & implementation

GLBASafeguards Rule Implementation

GLBA Safeguards Rule implementation, including risk assessment, information security program development, safeguards, policies and procedures, service provider oversight, remediation planning, and supporting compliance documentation.

Starting at$13,500One-Time Implementation Project

Standard Scope: FTC Safeguards Rule.

Learn About GLBA

Readiness & implementation

HIPAASecurity Rule Implementation

HIPAA Security Rule implementation, including the Security Risk Analysis, risk management, administrative, physical and technical safeguards, security policies and procedures, remediation planning, and supporting compliance documentation.

Starting at$16,000One-Time Implementation Project

Standard Scope: HIPAA Security Rule.

Learn About HIPAA

Readiness & implementation

NIST SP 800-53Rev. 5 Implementation

NIST SP 800-53 Rev. 5 implementation, including scope and baseline definition, control tailoring, gap assessment, policy and control development, implementation guidance, remediation tracking, and supporting compliance documentation.

Starting at$18,000One-Time Implementation Project

Standard Scope: One agreed NIST SP 800-53 Rev. 5 control baseline for one defined in-scope environment.

Learn About NIST

Readiness & implementation

ISO 27001Implementation

ISO/IEC 27001:2022 ISMS implementation, including scope definition, risk assessment and treatment, Statement of Applicability, policies and procedures, control implementation guidance, required ISMS documentation, and certification readiness.

Starting at$25,000One-Time Implementation Project

Standard Scope: One defined ISMS and certification scope.

Learn About ISO 27001

Internal audit

ISO 27001Internal Audit

Independent ISO/IEC 27001:2022 internal audit to evaluate the ISMS against applicable requirements, document audit results, and identify nonconformities and opportunities for improvement in preparation for certification or surveillance audits.

Initial Certification Internal AuditStarting at$3,500

Years 2 & 3 Surveillance Cycle Internal AuditStarting at$2,500

Standard Scope: One defined ISO 27001 ISMS and certification scope for an organization with 1–20 employees. Larger or materially more complex ISMS scopes may require adjusted pricing.

Learn About ISO 27001 Internal Audits

Payment Options

Implementation is a fixed-fee project engagement. Monthly payment options over 12 months are available.

Discuss Your Compliance Requirements

Pricing & Scope

Implementation starting prices are one-time project fees based on one framework, organizations with 1–20 employees, one primary in-scope environment, and typical small-business technology and operational complexity.

Final pricing is based on scope and may increase for larger organizations, multiple entities or environments, additional frameworks, additional SOC 2 Trust Services Categories, complex infrastructure, significant remediation requirements, or other material increases in scope. Organizations outside the standard scope should contact us for a customized quote.

Independent audit, certification, penetration testing, GRC platform, and other third-party costs are separate and are not included in the implementation pricing shown above.

Impact Managed Compliance

Getting Compliant Is Only the Beginning.

Controls need to operate. Policies need to stay current. Risks change. Vendors need review. Evidence needs to be maintained. Findings need remediation. Auditors and customers come back.

Impact Managed Compliance provides ongoing support to keep your compliance program operating, current, and ready throughout the year.

Managed Compliance is optional and can begin after implementation or be used by organizations that have completed their initial compliance effort but need ongoing help managing the program.

Managed Compliance pricing is based on one primary compliance framework, organizations with 1–20 employees, one primary in-scope environment, and a defined standard scope.

Standard framework scope generally includes SOC 2 Security only, HIPAA Security Rule, FTC GLBA Safeguards Rule, an agreed NIST SP 800-53 Rev. 5 baseline, or one defined ISO 27001 ISMS scope.

Additional frameworks, SOC 2 Trust Services Categories, entities, environments, significant vendor volumes, extensive security questionnaires, or other material increases in scope are priced separately.

Why Impact Risk Advisors

Practical Compliance. Experienced Guidance.

Tailored, Not Generic

Policies, risks, controls, and compliance activities are developed around your actual organization, systems, and requirements rather than generic templates.

More Than Control Monitoring

We help with the work behind the framework, including policies, risk assessments, control design, evidence, vendor risk, remediation, and audit readiness.

Technology Flexible

Already have a GRC platform? We can work within it. Need one? We can help implement and administer it. Don't need one? We can manage the program without requiring expensive dedicated compliance software.

Experienced Guidance

Senior-level experience across cybersecurity compliance, IT audit, risk management, security governance, and assurance.

Louis Van Der Westhuizen, Founder of Impact Risk Advisors

Founder-Led Expertise

Nearly Two Decades of Audit, Risk & Compliance Experience

Impact Risk Advisors was founded by Louis Van Der Westhuizen, bringing nearly two decades of cybersecurity, IT audit, risk management, and compliance experience, including leadership experience within major assurance and advisory practices.

CISSPCISACIAISO 27001 Lead Auditor

Impact Risk Advisors combines senior-level compliance expertise with specialized resources where needed, providing experienced support without the overhead and complexity of a large consulting firm.

About Impact Risk Advisors

Client Testimonials

What Our Clients Say

Real feedback from organizations we've supported across SOC 2, HIPAA, GLBA, and broader cybersecurity compliance programs.

Our experience with Impact Risk Advisors has been outstanding. They've helped us strengthen our HIPAA compliance, risk management, and vendor due diligence efforts with expert, practical guidance. Their support is responsive, thoughtful, and always aligned with our specific needs. Highly recommended for any organization needing hands-on compliance support.

JS

Jay Sachdev

CTO, Mosio

Our experience working with Impact Risk Advisors has been excellent. They provided practical guidance throughout our GLBA and SOC 2 compliance efforts and helped us strengthen our overall security and compliance program. Their approach was responsive, knowledgeable, and tailored to our organization's needs. We highly recommend them to companies navigating complex compliance requirements.

SJ

Sid Jain

Co-Founder, Pathfinder

Impact Risk Advisors has been a valuable partner in supporting our SOC 2 compliance journey. Their team provides responsive, thoughtful guidance and helps keep our compliance efforts organized and manageable. We appreciate their practical approach and ongoing support throughout the implementation process.

JR

Jacob Riff

Founder & COO, Klaay

Ready to Make an Impact on Your Compliance Program?

Whether you need to build a compliance program or keep an existing program operating, start with a conversation about where you are today.

Schedule a Consultation